Independent security consulting

Certainty where the stakes are highest

GreyOps protects confidential information at the very highest level. For executives of public and private organisations, we secure rooms against data leakage, eavesdropping and observation: from sweep and security awareness to high-assurance information security.

Services

Independent, discreet and methodologically sound

GreyOps provides specialised counter-espionage, built on years of experience in national security. We make hidden leakage and eavesdropping risks visible, substantiated and manageable. We do that in sensitive rooms and objects, for sensitive transactions, board decisions, critical assignments or other occasions. Mostly for clients with ABRO contracts, obligations under the Dutch Cybersecurity Act or the Dutch Trade Secrets Protection Act. We provide awareness sessions and training so that organisations can take lasting steps in security awareness.

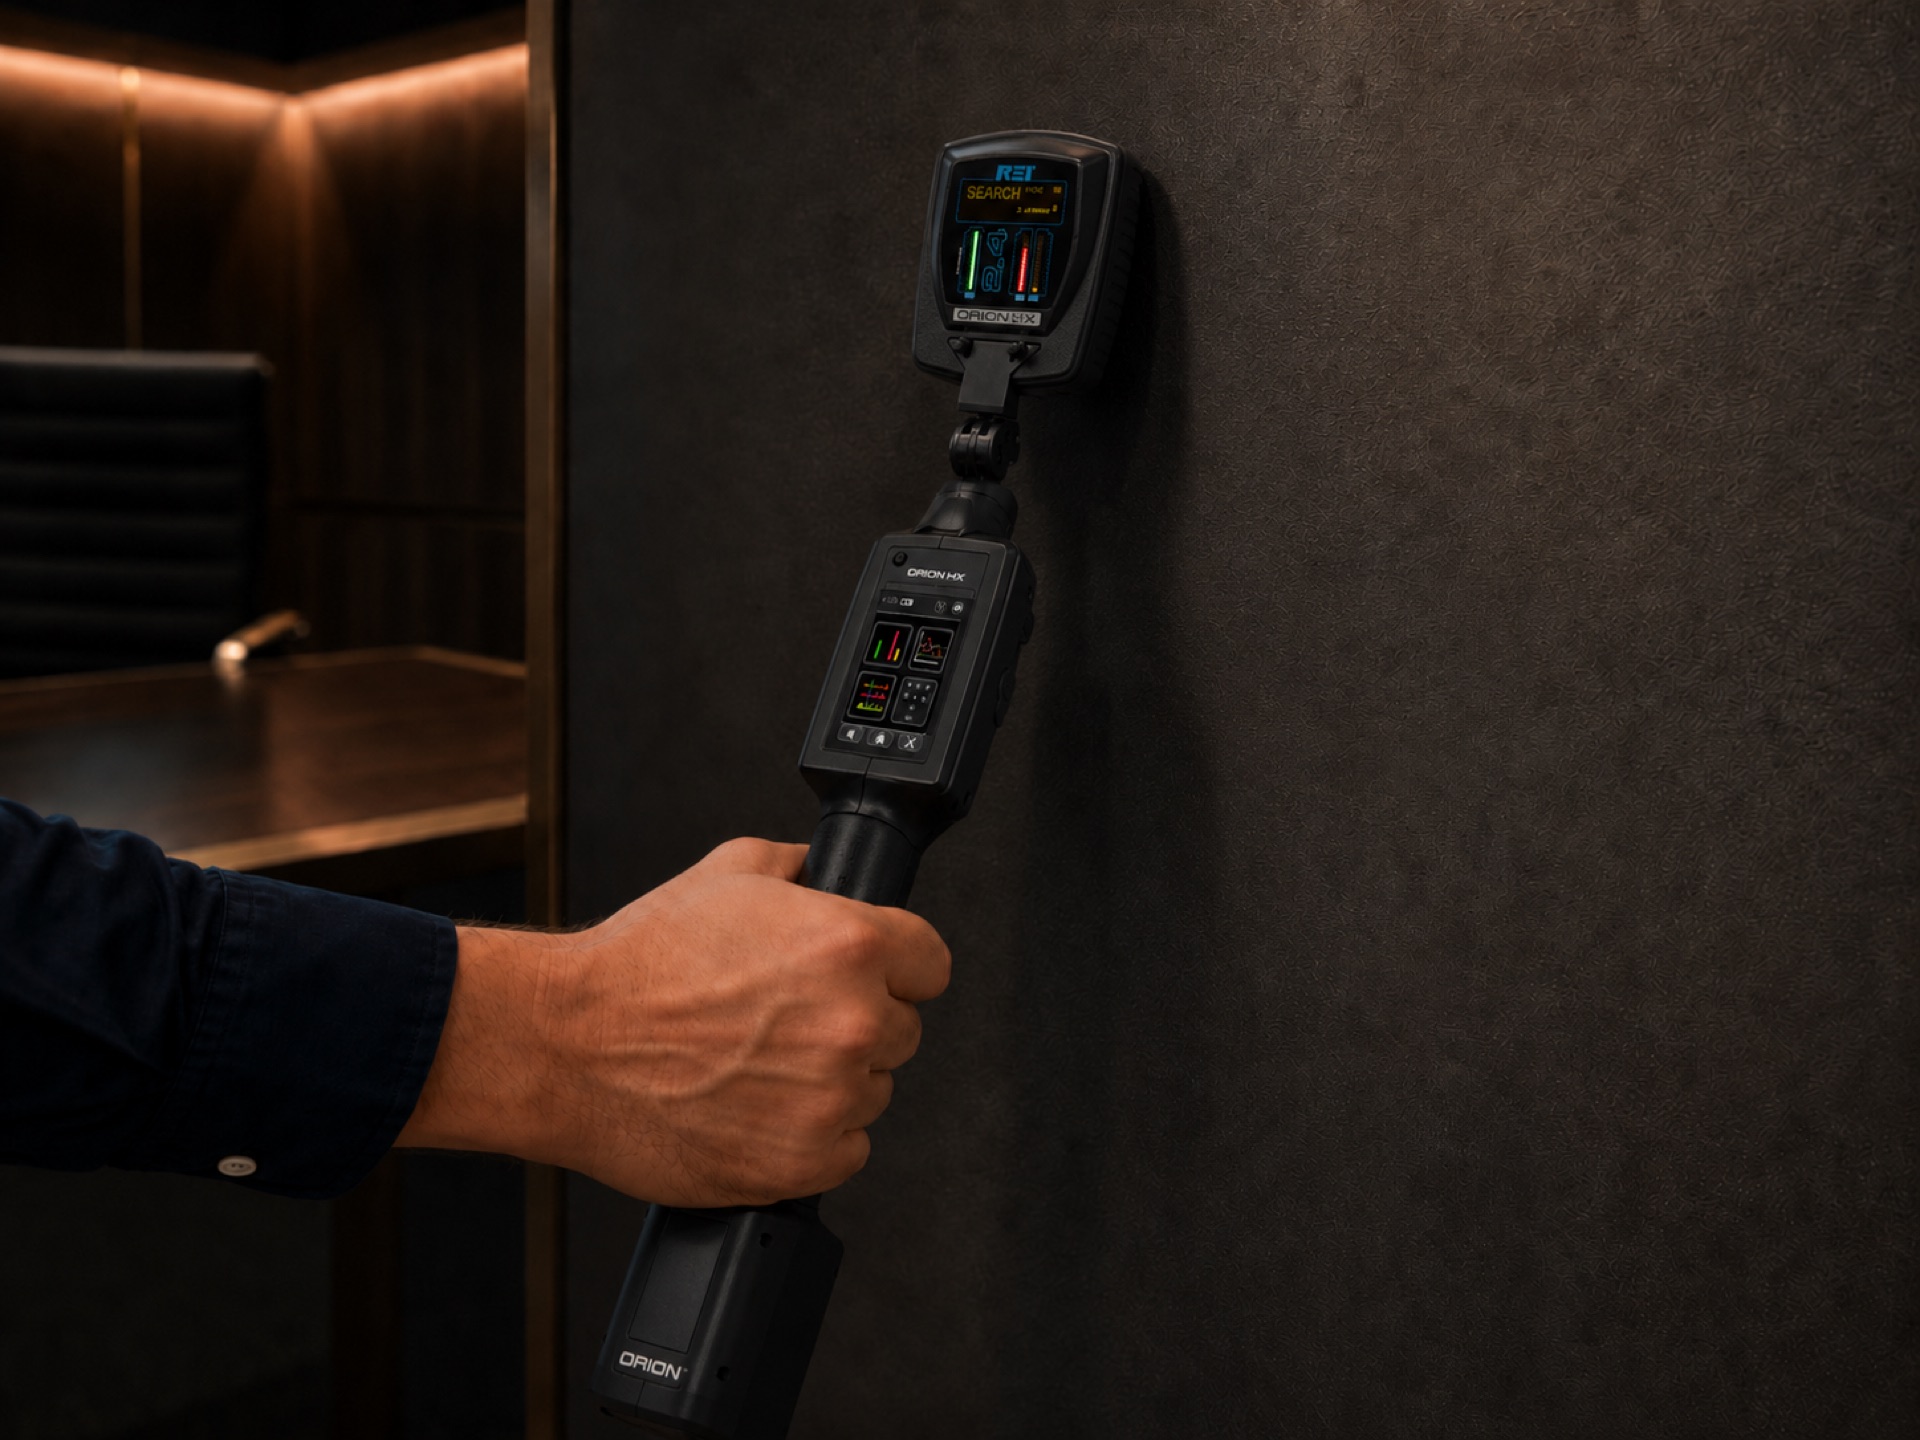
Measurement equipment during a TSCM sweep on a boardroom table

Electronic security surveys

Sweeps of boardrooms, executive offices, R&D spaces and vehicles for eavesdropping devices and unwanted signals. Performed with high-grade detection equipment and from a working knowledge of advanced attack methods. Reported at board level, methodologically sound.

Read more: TSCM sweeps
Entrance to a secure meeting room

Security consulting

Design and assessment of secure rooms: from meeting rooms with elevated requirements to fully shielded environments, including organisational assurance in procedures and awareness.

Read more: Security consulting
Boardroom with a presentation screen reading TEMPEST/EMSEC

Awareness and training

Awareness programmes on espionage, for boards and operational audiences alike. We cover technical and human countermeasures in a mix that suits the audience, working through concrete hybrid-threat scenarios, leading to greater resilience.

Read more: Awareness and training
Why a sweep

What is being found

Eavesdropping is not a theoretical risk. At companies, governments and international institutions, eavesdropping devices are found in furniture, fittings, ventilation, cabling, computer systems and peripherals.

Observation equipment is deliberately hard to recognise, and the period between placement and discovery (dwell time) is usually months. Detection does not usually happen by chance, but through targeted examination. Far more often, exposure arises without any malicious intent, through legitimate equipment that unintentionally gives away information or makes unwanted communication possible. The methodical GreyOps approach is aimed at examining both categories systematically: concealed eavesdropping and observation devices, and technical signals/equipment that does not fit the expected picture. The link below sets out a selection of documented cases.

Read more: publicly documented cases

Technical experts, not salespeople

Independent

We hold no vendor interest. Our advice serves one purpose: strengthening your resilience for the long term.

Scientific

Extensive professional experience in national security, with a doctorate in security sciences (PhD).

Discreet

Confidentiality is not an empty slogan; it is built into every engagement from the first contact.

For organisations where confidentiality carries real weight

Our clients fall into three segments with one common denominator: information that must not leak. The reason may be a legal obligation or a risk profile. Beyond that, specific processes, sensitive rounds of talks or rooms used routinely for confidential discussion.

Compliance

Organisations falling under the Dutch Cybersecurity Act, the ABRO or the Dutch Trade Secrets Protection Act, or operating in adjacent critical supply chains, that want and need to show their resilience is in order.

Sensitive sectors

Law firms, M&A advisory, AI and technology companies with high-value IP, semiconductor and defence suppliers, family offices and boards engaged in confidential, strategic negotiations.

High-risk profiles

Executives, publicly known individuals, (foreign) delegations and research institutions, or where there are concrete indications of eavesdropping, data leaks, insider risk or economic espionage.

According to the AIVD annual report 2025 (the Dutch General Intelligence and Security Service), the threat from states with offensive cyber programmes is greater than before, and economic espionage risk has increased.